介绍
在一些特定的情况下nginx需要限制用户的访问例如根据一下条件:根据IP,根据用户,根据请求方法等··
方式1:通过location里面IP限制请求,被限制请求返回403,如果要ipv6的限制编译安装的时候需要编译·· --with-ipv6··
语法:(allow|deny·· address | CIDR | unix: | all;
作用域: http, server, location, limit_except
举例:限制ip:除··192.168.1.158不可以访问,··192.168.1.0/24”网段其他用户可以访··,除此之外的其它ip不可以访问··
    server {
        ...
        deny  192.168.1.158;
        allow 192.168.1.0/24;
        deny  all;
    }
根据用户名密码限··
创建密码文件
    [root@localhost nginx-new]# htpasswd -c ./passwdfile  admin  #添加用户名为admin
    New password:                        #此处输入密码
    Re-type new password:          #再次输入密码
    Adding password for user admin
    [root@localhost nginx-new]# cat passwdfile
    admin:tKAyBpIh8xdyk
    [root@localhost nginx-new]# mv passwdfile conf/
            location /images/
            {
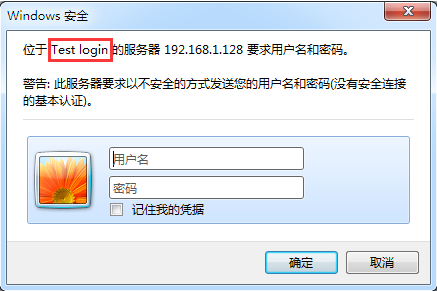
                    auth_basic           "Test login";
                    auth_basic_user_file passwdfile;
                    root /usr/local/kafka/html;
            }
请求地址images/aaa.jpg
** satisfy 让你更加灵活使用多种验证方式**
允许访问如果所··(all)或至少一··(any)模块通过验证才可以访问。( ngx_http_access_module, ngx_http_auth_basic_module or ngx_http_auth_request_module··
默认是: satisfy all;必须通过所有验··
语法·· satisfy [ all | any ]
使用字段:http, server, location
在下面配置里面使用了access模块和auth basic模块验证·· satisfy any;就是说只要匹配到两种模块中的一种便可以正常访问
            location /images/
            {
                     satisfy any;
                   deny  192.168.1.1;
                   deny  all;
                    auth_basic           "Test login";
                    auth_basic_user_file passwdfile;
                    root /usr/local/kafka/html;
            }
nginx教程